Valid Test Simulate materials for certificate qualification
 
[Jan 10, 2024] Today Updated 1z0-1104-23 Exam Dumps Actual Questions [Q61-Q85]

[Jan 10, 2024] Today Updated 1z0-1104-23 Exam Dumps Actual Questions [Q61-Q85]

4/5 - (1 vote)

[Jan 10, 2024] Today Updated 1z0-1104-23 Exam Dumps Actual Questions

1z0-1104-23 exam dumps with real Oracle questions and answers

Oracle 1z0-1104-23 Exam Syllabus Topics:

Topic Details
Topic 1
  • Understand MFA, Identity Federation, and SSO
  • Describe OCI Shared Security Responsibility Model
Topic 2
  • Use threat intelligence to identify rogue users
  • Configure security for OCI storage services
Topic 3
  • Implement conditional and advanced policies
  • Configure Dynamic Groups, Network Sources, and Tag-Based Access Control
Topic 4
  • Discuss core security services offered by OCI
  • Configure security for Oracle Autonomous Database and DB Systems
Topic 5
  • Describe key capabilities provided by Data Safe
  • Describe the use case for auditing and review OCI Audit Logs


NO.61 A company needs to have somebuckets as public in the compartment. You want Cloud Guard to ignore the problem associated with public bucket. Select TWO correct answers


NO.62 As a security administrator, you found out that there are users outside your co network who are accessing OCI Object Storage Bucket. How can you prevent these users from accessing OCI resources in corporate network?


NO.63 What do the features of OS Management Service do?


NO.64 What does the following identity policy do?
Allow group my-group to use fn-invocation in compartment ABC where target.function.id = ‘<function-OCID>’


NO.65 What are the two items required to create a rule for the Oracle Cloud Infrastructure (OCI) Events Service? (Choose two.)


NO.66 Which statements are CORRECT about Multi-Factor Authentication in OCI ? Select TWO correct answers


NO.67 What does an audit log event include?


NO.68 What is the matching rule syntax for a single condition?


NO.69 When using Management Agent to collect logs continuously, which is therequired configuration for OCI Logging Analytics to retrieve data from numerous logs for an instance?


NO.70 Challenge 4 – Task 6 of 6
Configure Web Application Firewall to Protect Web Server Against XSS Attack Scenario You have to protect web applications hosted on OCI from cross-site scripting (XSS) attacks. You can use the OCI Web Application Firewall (WAF) capabilities to create rules that compare against incoming requests to determine if the request contains an XSS attack payload. If a request is determined to be an attack, WAF should return the HTTP Service Unavailable (503) error.
To ensure that the configured WAF blocks the XSS attack, run the following script: [http://<public- ip-enforcement-point>/index.html?<p style=”background:url(javascript:alert(1))”](http://<public- ip-enforcement-point>/index.html?<p style=”background:url(javascript:alert(1))”>) To complete this deployment, you have to perform the following tasks in the environment provisioned for you:
Configure a Virtual Cloud Network (VCN)
Create a Compute Instance and install the Web Server
Create a Load Balancer and update Security List
Create a WAF policy
Configure Protection Rules against XSS attacks
Verify the created environment against XSS attacks

Note: You are provided with access to an OCI Tenancy, an assigned compartment, and OCI credentials. Throughout your exam, ensure to use the assigned Compartment 99233424-C01 and Region us-ashburn-1.
Complete the following task in the provisioned OCI environment:
You will connect to the web server and append an XSS script. The protection rule will evaluate the requests and respond accordingly.

NO.71 What must be configured for a load balancer to accept incoming traffic?


NO.72 Which OCI service canindex, enrich, aggregate, explore, search, analyze, correlate, visualize and monitor data?


NO.73 Which statement about Oracle Cloud Infrastructure Multi-Factor Authentication (MFA)is NOT valid?


NO.74 Which Cloud Guard component identifies issues with resources or user actions and alerts you when an issue is found?


NO.75 Which VCNconfiguration is CORRECT with regard to VCN peering within a same region ?


NO.76 Which statement about Oracle Cloud Infrastructure Multi-Factor Authentication (MFA)is NOT valid?


NO.77 Challenge 4 – Task 4 of 6
Configure Web Application Firewall to Protect Web Server Against XSS Attack Scenario You have to protect web applications hosted on OCI from cross-site scripting (XSS) attacks. You can use the OCI Web Application Firewall (WAF) capabilities to create rules that compare against incoming requests to determine if the request contains an XSS attack payload. If a request is determined to be an attack, WAF should return the HTTP Service Unavailable (503) error.
To ensure that the configured WAF blocks the XSS attack, run the following script: [http://<public- ip-enforcement-point>/index.html?<p style=”background:url(javascript:alert(1))”](http://<public- ip-enforcement-point>/index.html?<p style=”background:url(javascript:alert(1))”>) To complete this deployment, you have to perform the following tasks in the environment provisioned for you:
Configure a Virtual Cloud Network (VCN)
Create a Compute Instance and install the Web Server
Create a Load Balancer and update Security List
Create a WAF policy
Configure Protection Rules against XSS attacks
Verify the created environment against XSS attacks

Note: You are provided with access to an OCI Tenancy, an assigned compartment, and OCI credentials. Throughout your exam, ensure to use the assigned Compartment 99233424-C01 and Region us-ashburn-1.
Complete the following task in the provisioned OCI environment:
Create a WAF policy with the name IAD-SP-PBT-WAF-01_99233424-lab.user01 Eg: IAD-SP-PBT-WAF-01_99232403-lab.user02

NO.78 You subscribe to a PaaS service that follows the Shared Responsibility model.
Which type of security is your responsibility?


NO.79 your company has hired a consulting firm to audit your oracle cloud infrastructure activity and configuration you have created a set of users who will be performing the audit, you assigned these user to the orgauditgrp group. the auditor required the ability to see the configuration of all resources within tenant and you have agreed to exempt the dev compartment from the audit.
which IAM policy should be created to grant the orgauditgrp the ability to look at configuration for all resources except for those resources inside the dev compartment?


NO.80 Challenge 2
Least-Privileged Model Enforcement Leveraging Custom Security Zones
Scenario
In deploying a new application, a cloud customer needs to reflect different security postures. If a security zone is enabled with the Maximum Security Zone recipe, the customer will be unable to create or update a resource in the Security Zone if the action violates the attached Maximum Security Zone policy.
As an application requirement, the customer requires a compute instance in the public subnet. You, therefore, need to configure Custom Security Zones that allow the creation of compute instances in the public subnet.
To complete this deployment, you have to perform the following tasks in the environment provisioned for you:
* Create a Custom Security Zone recipe to allow compute instances in the public subnet.
* Create a Security Zone using the Custom Security Zone recipe.
* Configure a Virtual Cloud Network (VCN) and Public Subnet.
* Provision a Compute Instance in the public subnet.
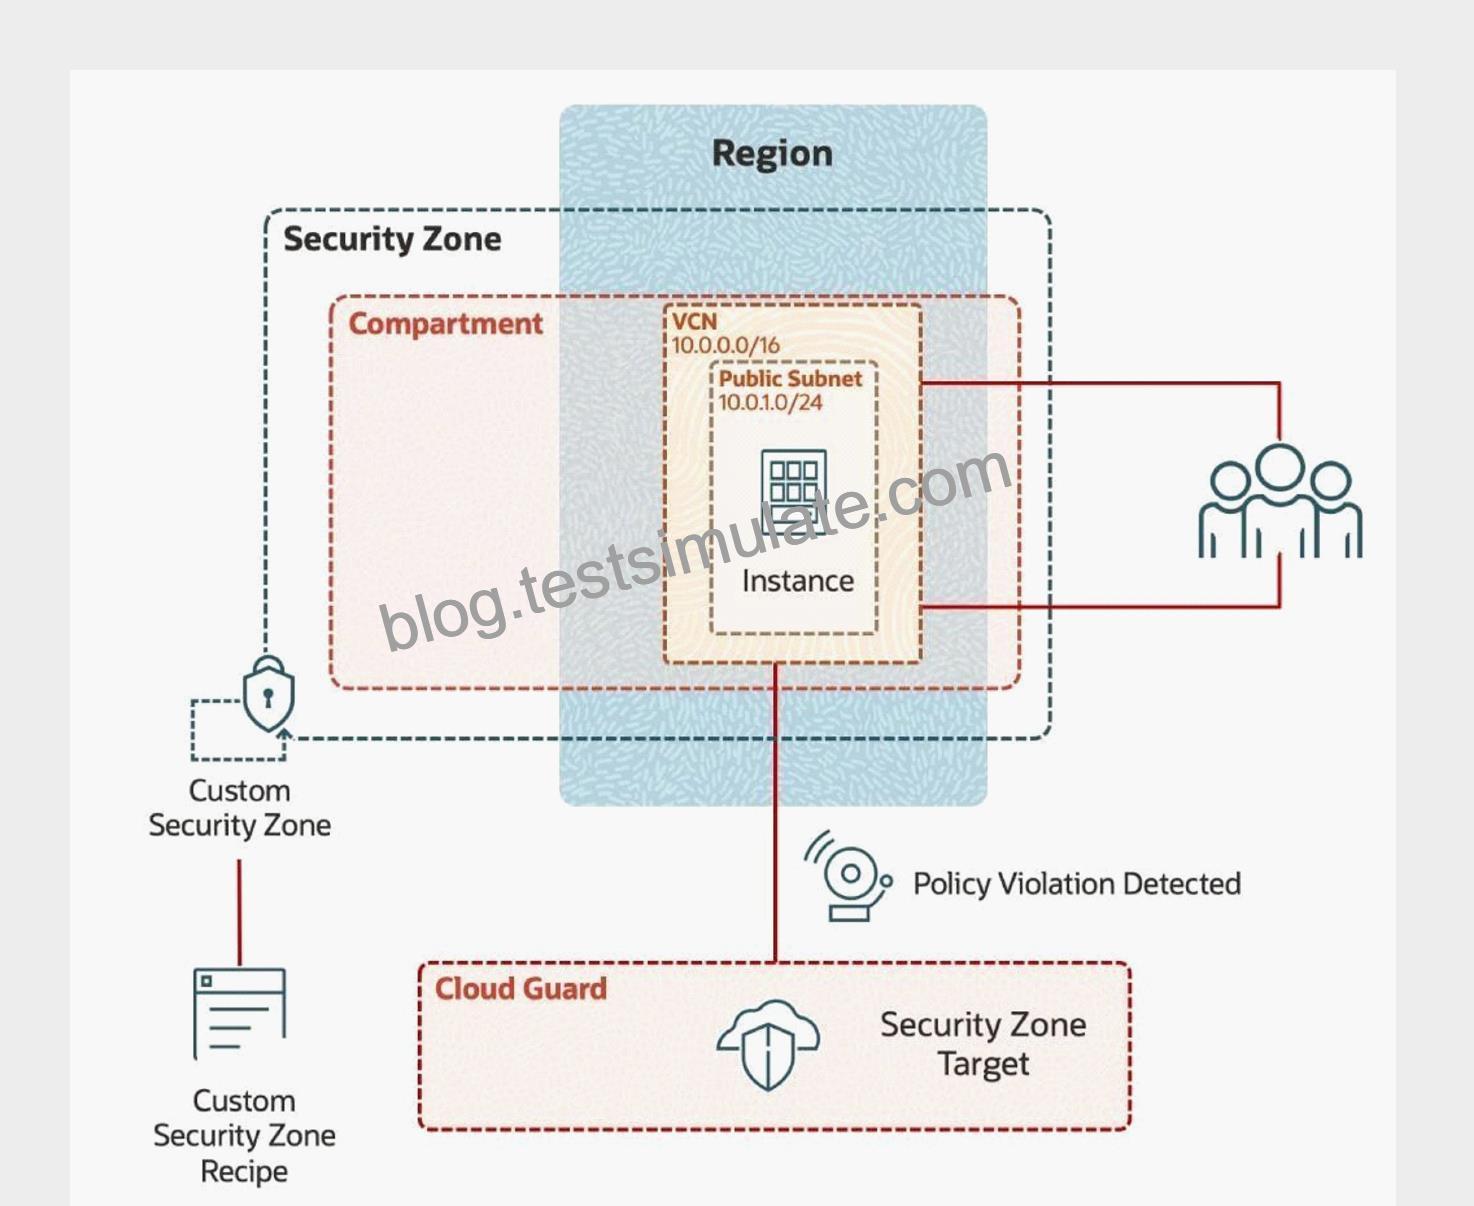
Note: You are provided with access to an OCI Tenancy, an assigned compartment, and OCI credentials. Throughout your exam, ensure to use the assigned Compartment 99234021-C01 and Region us-ashburn-1 Complete the following tasks in the provisioned OCI environment:
Create a Custom Recipe with the name
Create a Security Zone with the name
Create a VCN with the name IAD-SP-PBT-VCN-01
Create a Public Subnet with the name IAD-SP-PBT-PUBSNET-01
Create a Compute Instance with the name IAD-SP-PBT-1-VM-01, using the “Oracle Linux 8” image and “VM.Standard2.1” as shape

NO.81 When doesCloud Guard re-open an issue and update the history?


NO.82 Which Oracle Cloud Service provides restricted accessto target resources?


NO.83 As a Security Admin you want to inspect the metadata and actual data in your Oracle databases to discover sensitive data and provide comprehensive results listing the sensitive columns and related information. Which Data Safe feature will help you to achieve the above requirement ?


NO.84 You need to create matching rules for a conditional policy. Which TWO matching rules syntax can be used? (Choose two.)


NO.85 “Jazz Clothing” is an e-commerce company that wants to secure their in-transit communication to online store’s hosted on Oracle Cloud Infrastructure (OCI) by ensuring secure Transport Layer Security (TLS) connections. They plan to automate the process of creating and rotating certificates using the OCI Certificates service to avoid outages due to expired certificates. What is a key benefit that Jazz Clothing will gain by automating their certificate management for TLS connections in OCI? (Choose the best Answer.)


Exam Sure Pass Oracle Certification with 1z0-1104-23 exam questions: https://www.testsimulate.com/1z0-1104-23-study-materials.html

Related Links: myportal.utt.edu.tt www.stes.tyc.edu.tw myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt everlink.tools

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below