QUESTION 191
Which of the following cloud deployment model can be shared by several organizations?
In Community cloud, the cloud infrastructure is provisioned for exclusive use by a
specific community of consumers from organizations that have shared concerns (e.g.,
mission,security requirements, policy, and compliance considerations). It may be owned,
managed, and operated by one or more of the organizations in the community, a third party, or
some combination of them, and it may exist on or off premises.
For your exam you should know below information about Cloud Computing deployment models:
Private cloud
The cloud infrastructure is provisioned for exclusive use by a single organization comprising
multiple consumers (e.g., business units). It may be owned,managed, and operated by the
organization, a third party, or some combination of them,and it may exist on or off premises.
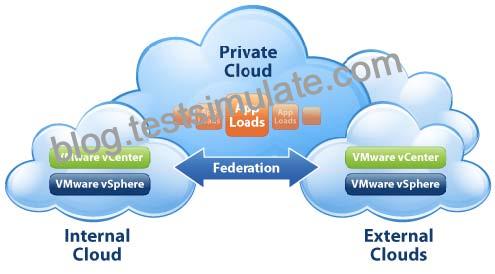
Private Cloud Image Reference – http://www.inflectionpoint.co.uk/Portals/5/VMware-vCloud.jpg
Community Cloud
The cloud infrastructure is provisioned for exclusive use by a specific community of consumers from organizations that have shared concerns (e.g., mission,security requirements, policy, and compliance considerations). It may be owned, managed, and operated by one or more of the organizations in the community, a third party, or some combination of them, and it may exist on or off premises.
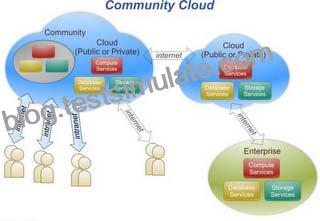
Community Cloud
Image Reference – http://cloudcomputingksu.files.wordpress.com/2012/05/community-cloud.png
Public Cloud
The cloud infrastructure is provisioned for open use by the general public. It may be owned,
managed, and operated by a business, academic, or government organization, or some
combination of them. It exists on the premises of the cloud provider.
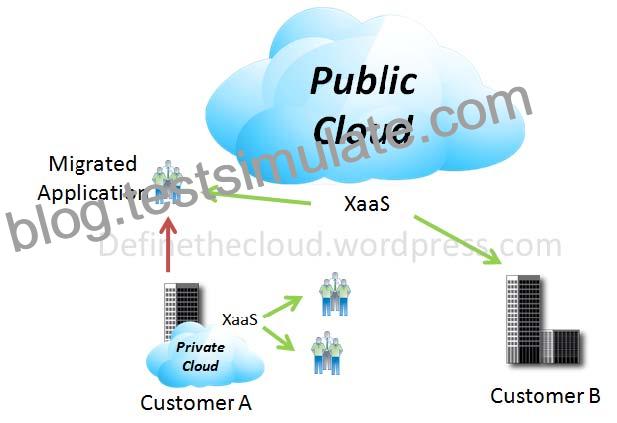
Public Cloud
Image reference – http://definethecloud.files.wordpress.com/2010/04/image3.png
Hybrid cloud The cloud infrastructure is a composition of two or more distinct cloud infrastructures (private, community, or public) that remain unique entities, but are bound together by standardized or proprietary technology that enables data and application portability (e.g., cloud bursting for load balancing between clouds)
hybrid cloud Image reference – http://www.virtualizationpractice.com/wp-content/uploads/2013/04/Hybrid-Cloud-Computing-Solution1.jpg
The following answers are incorrect: Private cloud – The cloud infrastructure is provisioned for exclusive use by a single organization comprising multiple consumers (e.g., business units). It may be owned,managed, and operated by the organization, a third party, or some combination of them,and it may exist on or off premises.
Public cloud – The cloud infrastructure is provisioned for open use by the general public. It may be owned, managed, and operated by a business, academic, or government organization, or some combination of them. It exists on the premises of the cloud provider.
Hybrid cloud – The cloud infrastructure is a composition of two or more distinct cloud infrastructures (private, community, or public) that remain unique entities, but are bound together by standardized or proprietary technology that enables data and application portability (e.g., cloud bursting for load balancing between clouds)
The following reference(s) were/was used to create this question: CISA review manual 2014 page number 102 Official ISC2 guide to CISSP 3rd edition Page number 689 and 690